PHP2Shell: update PHP on your web servers today
On 21st October, the PHP project released emergency fixes for two critical security flaws in the PHP programming language. PHP runs most of the web, including most WordPress, Drupal, Joomla and Magent
Insights
Real incident write-ups, threat actor analysis, regulatory commentary, and engineering deep-dives from our SOC, offensive team, and advisory practice. No vendor pitches, no fear-mongering.
Written by the same people who run real engagements.
Latest articles
On 21st October, the PHP project released emergency fixes for two critical security flaws in the PHP programming language. PHP runs most of the web, including most WordPress, Drupal, Joomla and Magent
Responsible Disclosure Disclaimer: Syndis delayed the publication of these results until all identified parties had been notified of the situation and given a chance to remediate. What Companies in th
Financial entities follow DORA. Most other medium and large organisations in critical sectors follow NIS2. Some follow both. Here is how to tell which applies to you, and what changes when it does.
Most of us can probably agree that organizations of all sizes and industries have these things in common: Stale service accounts, old API keys, and other non-human identities that are running in their

We are thrilled to share some exciting news with our community: Petra Klein joines the Syndis leadership team as Managing Director (VD) of Syndis in Sweden on October 1st.
We’ve all been trained to trust search engines. Need to download a PDF editor, an open-source video converter, or the latest AI companion desktop app? You type it into the search bar, click the very f
Over the past few days, cybersecurity experts at Syndis have been grappling with what appears to be one of the most complex and sophisticated cyberattacks the company has investigated to date. Strong evidence suggests that the attack methodology was developed with the assistance of a Large Language Model (LLM), despite the safety guardrails typically built into these models to prevent such misuse.
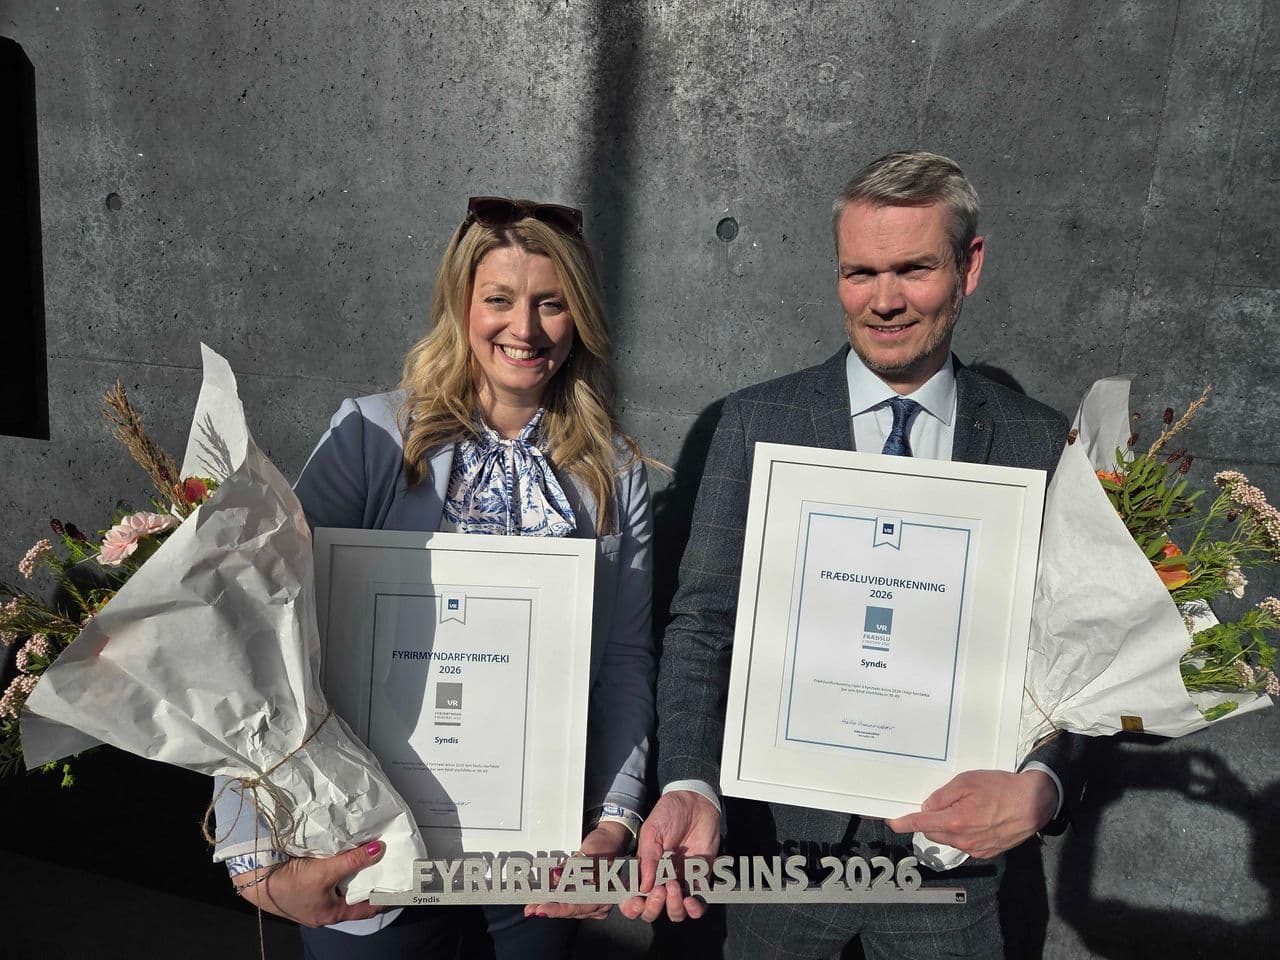
Both recognitions come directly from employee feedback in VR's annual workplace survey.
We are proud to announce our partnership with Dediko A/S, one of Denmark's most trusted names in IT security.
We are excited to announce that Syndis and Abero Finland are expanding and opening a joint operation in Helsinki!
Compliance without security rarely holds up. It should strengthen an organization's actual security posture, not just create paperwork for audits.
The media hype around AI-driven vulnerability discovery is deafening right now, especially following the news of Anthropic's Mythos and Project Glasswing. But what does the actual technical data tell us?
Most of what we publish starts as a client conversation. If something resonates, talk to us
We respond to most inquiries within one business day.